WannaCry: The Ransomware Attack That Crippled the NHS
How a global cyberattack on May 12, 2017 paralyzed Britain's healthcare system and exposed critical vulnerabilities
Published June 6, 2025
Quick Facts
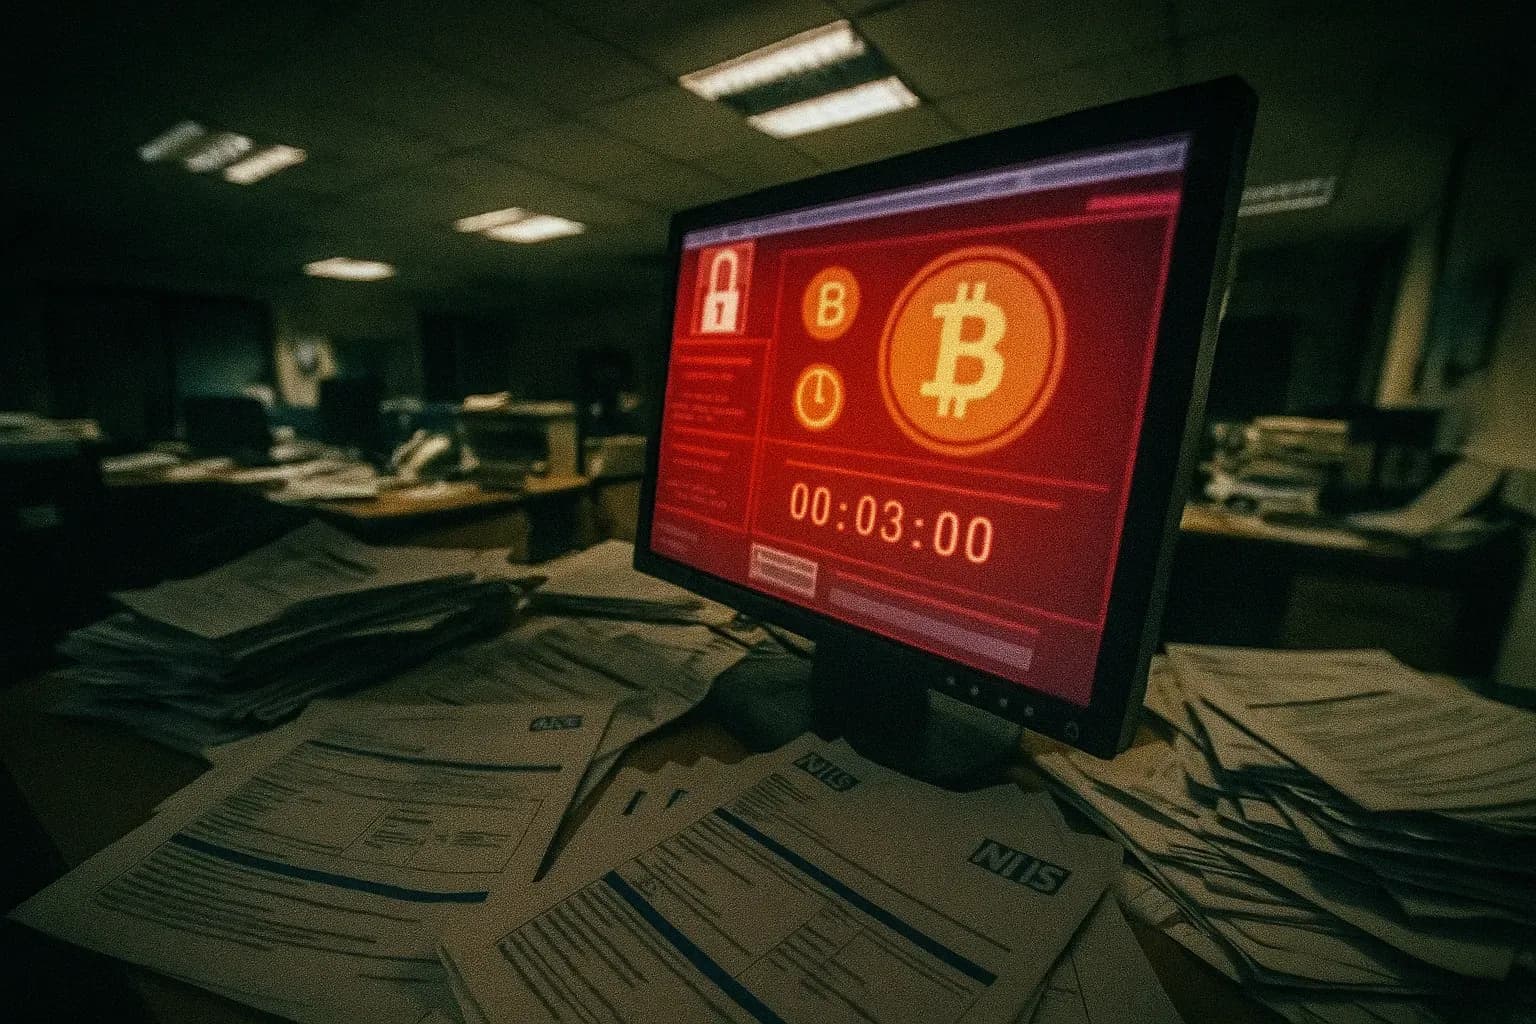
On Friday, May 12, 2017, Britain's National Health Service ground to a halt. The WannaCry ransomware—a variant exploiting a Microsoft Windows vulnerability previously discovered by the NSA and leaked by the Shadow Brokers—spread across healthcare networks worldwide. While the global attack would eventually impact more than 300,000 computers in 150 countries, the NHS became one of the most visible victims of the day.
The scale of the healthcare catastrophe was staggering. At least 80 of England's 236 NHS trusts were either directly infected or forced to shut down systems as a precaution. Beyond hospital networks, 603 additional primary care and NHS organizations fell victim, including 595 general practice surgeries. Across all affected facilities, up to 70,000 devices were locked out—computers, MRI scanners, blood-storage refrigerators, and theatre equipment all rendered inaccessible.
For patients and staff, the consequences were immediate and severe. The ransomware locked healthcare workers out of their systems, preventing access to patient records, test results, and critical information needed for discharges and transfers. Thousands of non-urgent surgeries and appointments were cancelled. Ambulance services diverted patients to other facilities, turning away non-critical emergencies. Some trusts, including East and North Hertfordshire NHS, saw their telephone systems collapse entirely.
Timeline
WannaCry attack begins and spreads globally
On 12 May 2017, the ransomware worm WannaCry begins to spread. Within a few hours, computers in over 150 countries are infected. The NHS declares a 'major incident' the same day.
NHS declares 'major incident'
The British healthcare service declares a 'major incident' on 12 May 2017. At least 80 NHS trusts and 603 other NHS organisations are affected in England.
National Audit Office publishes report on attack
The British National Audit Office publishes an investigative report in October 2017 on the WannaCry attack and its consequences for the NHS.
UK authorities attribute attack to North Korea
British authorities and the NCSC officially attribute the WannaCry attack to North Korea and the Lazarus Group as the most likely actor. The exact date of the official statement is not specified in the sources.
NHS England publishes internal lessons report
In February 2018, NHS England publishes an internal evaluation of the attack, focusing on lessons learned and prevention of future attacks.
In a striking reversion to pre-digital medicine, NHS staff returned to pen-and-paper record-keeping. Staff members used personal mobile phones to communicate. Ambulance handover screens went dark, and patient transport booking portals disappeared offline. The attack had exposed how dependent modern healthcare had become on digital systems—and how vulnerable those systems remained.
The financial toll was substantial. The NHS estimated the attack cost £92 million in total damage: £19 million from cancelled operations and appointments, plus £73 million in IT recovery and system repairs. No NHS organization paid the ransom, and critically, no patient data was compromised or stolen.
Investigations revealed the NHS was particularly vulnerable. Many systems ran outdated software: Windows 7 remained prevalent across the service, while the NHS claimed only 4.7% of devices still used the even older Windows XP—a figure that drew skepticism from cybersecurity experts. Microsoft had released patches for the vulnerability in March 2017, two months before the attack, but many NHS trusts had not applied them. The virus spread via the N3 network rather than NHSmail, and while the NHS was not specifically targeted, it became collateral damage in a global cyberattack.
The crisis was contained within 48 hours. By May 15, around 16 trusts remained affected. Between May 15 and mid-September 2017, a cybersecurity researcher activated a kill-switch in the malware code, preventing WannaCry from encrypting devices in some cases and effectively halting its spread.
UK Health Secretary Jeremy Hunt declared there would be no second wave, noting that 80% of the NHS remained unaffected and that patients should attend appointments unless told otherwise. Yet the attack had exposed systemic weaknesses. Following the incident, NHS Digital invested over £60 million in upgrades and planned an additional £150 million in improvements.
WannaCry served as a watershed moment for healthcare cybersecurity globally. It demonstrated that ransomware attacks were not merely financial crimes or corporate espionage—they were threats to public health itself. When hospital systems fall, lives hang in the balance.
Sources: - https://pmc.ncbi.nlm.nih.gov/articles/PMC5461132/ - https://www.blackfog.com/wannacry-ransomware-nhs-attack/ - https://www.acronis.com/en/blog/posts/nhs-cyber-attack/ - https://en.wikipedia.org/wiki/WannaCry_ransomware_attack - https://www.nao.org.uk/wp-content/uploads/2017/10/Investigation-WannaCry-cyber-attack-and-the-NHS.pdf
Ask about this case
Answers from KrimiNyt's coverage onlyFollow this case
Get an email when a new documentary, podcast or book about WannaCry: The Ransomware Attack That Crippled the NHS appears, or when a verdict is reached.